 ChiefGyk3D
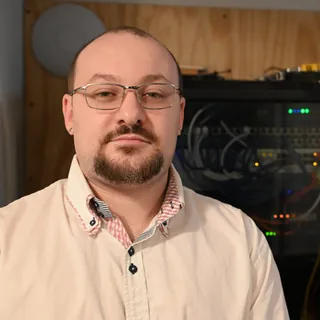
ChiefGyk3D
Senior Cybersecurity Engineer (CISSP)
Identity, Detection, Cloud, Network Defense, and Automation
Summary
Senior Cybersecurity Engineer and CISSP with about 15 years across IT and security. I design, build, integrate, and test security systems across identity, network defense, SIEM engineering, cloud security, zero trust, and automation. I question unnecessary access and use hands-on testing to check whether the design actually works.
I maintain open-source security tools and reusable CI workflows, and I share cybersecurity knowledge through tutorials, security breakdowns, and livestreams with more than 500,000 followers across YouTube, Twitch, Kick, and social platforms. My goal is to break down knowledge barriers.
Background
I’m a Senior Cybersecurity Engineer (CISSP), Linux nerd, ham radio operator, open-source builder, and content creator. I’m primarily self-taught. Most of what I know came from curiosity, building things in my homelab, and figuring out why they didn’t work.
My work spans identity and access management, endpoint security, security automation, zero trust, and cloud and network security. I also work with threat modeling, OSINT, telecom security, and SIEM/SOC tooling. That includes IAM, EDR, SOAR, ZTNA, and SASE, along with tools like pfSense, Suricata, Wazuh, and OpenSearch. I’m more than ready for a security architecture role, and that’s where I’m headed.
I run Linux on my desktops and servers, and my homelab is where a lot of my interests come together. It’s a production-style environment built partly from repurposed hardware, with a dual-GPU local AI box and self-hosted services including Mastodon, Matrix, and Pixelfed. Radio is part of that curiosity too, from software-defined radio to Meshtastic and LoRa. I care about end-to-end encryption, zero trust, owning my infrastructure, right to repair, and privacy rights.
- Desktop: Pop!_OS, Parrot OS, and Debian on hand-built desktops and laptops from Tuxedo Computers, System76, and MNT. Ubuntu on production servers.
- Radio: Licensed amateur radio operator. SDR, Meshtastic, LoRa, antenna builds, and a growing toolchain for turning a Linux box into an RF workstation.
- Self-hosted: My own Mastodon instance, Matrix homeserver, Pixelfed, link aggregator, support page, and more.
- Cares about: End-to-end encryption, zero trust, owning your infrastructure, right to repair, privacy rights, threat modeling, OSINT, and telecom security.
Skills
- Identity and access
- IAM, Single sign-on and MFA, Passwordless authentication with passkeys and hardware security keys, Identity-driven access controls, LDAP integration
- Detection and response
- EDR, SOAR, SIEM and SOC operations, Detection engineering
- Zero trust and cloud
- ZTNA and SASE, Cloud security, Zero trust
- Cloudflare
- Cloudflare Pages, Workers, R2, Email Routing, WAF custom rules, rate limiting and configuration rules, Wrangler, Content Security Policy, security headers, SHA-256-pinned scripts, immutable caching, build and post-deploy checks
- Network defense and systems
- Linux, Networking with pfSense, Suricata and UniFi
- Automation and code
- Python, Bash, PowerShell, Infrastructure as code with OpenTofu and Terraform, DevSecOps, Reusable GitHub Actions workflows with CI security checks
- Security practice
- Threat modeling, OSINT, Telecom security, Privacy, AI-assisted workflows
Tools and platforms
- Identity and access
- I work with single sign-on, MFA, passwordless authentication, passkeys, hardware security keys, identity-driven access controls, LDAP integration, and service authentication. Okta, Microsoft Entra, JumpCloud, YubiKey, Delinea.
- Endpoint, email, and data security
- I work across endpoint detection and response, email security, phishing response, data access visibility, and security platform automation. CrowdStrike, Proofpoint TRAP, Avanan, Varonis.
- Network security and zero trust
- I handle firewall administration, network segmentation, VLAN design and isolation, intrusion detection and prevention, DNS filtering, remote access architecture, network telemetry, and troubleshooting. Zscaler ZIA and ZPA, Twingate, pfSense CE and pfSense Plus, Suricata, pfBlockerNG, UniFi, MikroTik.
- Security operations and investigation
- My work includes log collection, forwarding, and analysis, security telemetry, detection, vulnerability management, honeypots and deception, and attack surface analysis. Splunk, Wazuh, OpenSearch, Datadog, Tenable, Wiz, VirusTotal, urlscan, OWASP Threat Dragon.
- Cloud, infrastructure as code, and secrets
- I build automated infrastructure, manage secrets, design zero-trust access for cloud environments, and create reproducible security labs and educational infrastructure. AWS, DigitalOcean, Terraform, OpenTofu, Spacelift, Doppler, GitHub, Cloudflare.
- Linux and homelab
- In my homelab, I administer Pop!_OS, Ubuntu, Debian, and Parrot OS systems, run virtualized infrastructure with Proxmox, repurpose hardware for services, and perform serial-console installations. I self-host Mastodon, Matrix, and Pixelfed, including Matrix-Discord bridging.
- Software and automation
- I develop Python tools and open-source libraries, build API integrations and event-driven bots, connect notification and messaging systems, and use GitHub-based development and code review. My CI work includes security checks, dependency scanning, and linting. GitHub, GitHub Copilot, Snyk, Discord and Matrix integrations, streaming and social-platform integrations.
- Local AI and agents
- I run local models through Ollama on a dual-GPU server and route work between local and hosted models based on cost and capability. I coordinate agents for drafting, implementation, and review, require human approval for paid model use, and use AI-assisted review alongside conventional CI and security checks.
- Radio, RF, and telecom
- I work with SDR, Meshtastic, LoRa, APRS and packet radio, RF experimentation, cellular modem integration, and telecom security. HackRF, Meshtastic devices, LoRa radios, and Linux-based radio and SDR tooling.
- Where I'm headed
- I am a Senior Cybersecurity Engineer with a CISSP, primarily self-taught through homelabbing and hands-on work. I am moving toward a security architecture role.
This site is the proof
I built this site on Cloudflare Pages, and the security headers include a strict CSP with hashed scripts pinned by SHA-256. The build checks and post-deploy smoke test verify the served script hashes; that smoke test caught a Cloudflare rewrite that injected a script. Fingerprinted assets use immutable caching, and build checks fail when page budgets are exceeded, including the 150 KB page budget. Locally, Lighthouse scores 100 on every indexable page type.
Selected accomplishments
- Zero trust infrastructure
- I built a locked-down DigitalOcean environment with OpenTofu and Spacelift, storing secrets in Doppler and restricting access through Twingate. I added a policy that blocks firewall rules open to the internet and fails closed on unknown values.
- Identity event visibility
- I built a Python poller that sends JumpCloud Directory Insights events to Wazuh as JSONL, bringing directory and access activity into the SIEM.
- SIEM operations
- I assembled a Dockerized SIEM and SOC stack with Wazuh, OpenSearch, Logstash, Grafana, and N8N workflows for alert triage and routing.
- Cloudflare site security
- I added strict security headers and checks that verify pinned script hashes during builds and after deployment. I built smoke checks for response status, headers, redirects, hashes, and served markup, and fixed an email rewrite they caught.
- Shared CI and release workflows
- I rolled out shared GitHub Actions workflows for linting, tests, container builds, signed releases, and scans, with a single CI gate across projects. I designed secret retrieval through OIDC and pinned workflow references to full commit SHAs.
- Open security education
- I built a free, open-source wiki of lessons, flowcharts, and exercises that teach zero trust, DevSecOps, and infrastructure as code. The material is available for anyone to read and try in their own accounts.
Open-Source Projects
Everything I build is open source. Fork anything, send PRs, open issues, or just say hi.
- Clouds Against Humanity: An open-source cloud security lab where you build and secure the infrastructure yourself with OpenTofu, Spacelift, Doppler, and Twingate. It has no public inbound ports.
- SIEM Docker Stack: A containerized OpenSearch and Wazuh SIEM that I run, with logging, monitoring, dashboards, and long-term data storage.
- pfSense SIEM Stack: The network side of my SIEM, built around pfSense, Suricata, network telemetry, and security automation.
- git-your-ship-together: Reusable GitHub Actions workflows with CI security checks, which I maintain and share across my Python projects.
- Skid Finder: A defensive toolkit that detects scripted Bluetooth Low Energy (BLE) spam and helps track down its source at conferences. That tracking is a foxhunt, the radio game of locating a hidden transmitter.
- Stream Daemon: Announces live streams from Twitch, YouTube, and Kick to Mastodon, Bluesky, Discord, and Matrix.
- Reach Around: In development: an open-source, privacy-first link page for creators, with analytics and a media kit.
- Hammunition: Open-source tooling that turns Debian-family Linux systems into amateur radio and RF workstations.
- Penguin Overlord: A Discord bot for tech enthusiasts, ham radio operators, aviation spotters and security professionals, with tech quotes, XKCD comics, solar weather data, radio news and event reminders.
- Star-Daemon: Monitors your GitHub starred repositories and posts updates to Mastodon, Bluesky, Discord and Matrix.
- Typo Sniper: An async typosquatting and domain threat intelligence scanner that detects lookalike domains, with URLScan, Doppler and AWS Secrets Manager integration.
- FrankenLLM: Runs different LLM models across multiple NVIDIA GPUs.
- NetPulse: Monitors internet connection speed, latency, jitter and packet loss, with automatic ISP failover detection.
- Department of Internal Arguments: AI agent personas and domain packs for Claude Code, Copilot, ChatGPT and local models, with measurements of what works.
- Scrum Around and Find Out: Board as code for GitHub Projects, a bring-your-own-App Action that keeps it current, and a playbook for running Claude, Codex and Copilot as one team.
- The Great InfoCon Recovery: Rebuilds and maintains a local copy of the infocon.org archive and DEF CON's media.defcon.org, with resumable downloads and SHA-256 hashes in a manifest.
- Patch-Gremlin: Sends Discord, Microsoft Teams, Slack or Matrix notifications when security updates are installed on Debian and RHEL-based systems.
Homelab and engineering practice
A production-grade home lab for building, breaking, and learning. I use single-board computers and repurposed hardware wherever practical.
- Network and security
- A Supermicro E300-8D firewall running pfSense, Suricata IDS/IPS, and pfBlockerNG on VLAN-segmented networks. UniFi managed switches and access points send telemetry into Grafana and InfluxDB through UniFi Poller, and device logs go to Wazuh for EDR alerting.
- SIEM server
- A Supermicro SuperServer 5019A-FTN4 with an Intel Atom C3758 and 64 GB of DDR4 ECC, on tiered SSD and NVMe storage. It runs a Dockerized OpenSearch hot/warm cluster with Wazuh, Grafana, Logstash, Prometheus, InfluxDB, Syslog-ng, UniFi Poller, and Portainer. siem-docker-stack pfsense-siem-stack
- AI inference
- The FrankenLLM server runs two GPUs, an NVIDIA RTX 5060 Ti 16 GB and an NVIDIA RTX 3050 8 GB, for simultaneous multi-model inference. FrankenLLM
- Compute and storage
- Raspberry Pi 4 and 5, Pine64, and other single-board computers for power-efficient computing. Second-hand PCs repurposed whenever possible to reduce e-waste. A Synology NAS with NUT (Network UPS Tools) monitoring and notifications.
- Radio, SDR, and time
- Meshtastic nodes, LoRa experiments, and custom antenna builds. SDR for ADS-B aircraft tracking, UAT weather, and RF signal analysis. Hammunition builds the workstation, and Hammunition Hill watches propagation from it. In progress: two GPS-disciplined stratum-1 NTP appliances built from Mother Ticker. Hammunition Hammunition Hill Mother Ticker
- Cloud extension
- Clouds Against Humanity: DigitalOcean droplets managed with OpenTofu through Spacelift, secrets in Doppler, and reachable only over Twingate zero-trust access with zero public inbound ports. Clouds Against Humanity
Certifications
- CISSP, earned in 2024
- CompTIA Security+, earned February 2026
- CompTIA Network+, earned February 2026
- CompTIA A+, earned February 2026
- Yes, the order is odd. CISSP came first, in 2024. I earned all three CompTIA certs in February 2026 while working toward my WGU bachelor's.
Education
- Working toward a bachelor's degree at WGU
- Associate degree in Network System Administration, ITT Tech, 2016
Speaking and community
- Cybersecurity creator with more than 500,000 followers across YouTube, Twitch, Kick, and social platforms.
- I make tutorials, security breakdowns, and livestreams with the goal of breaking down knowledge barriers.
- Open-source maintainer: I build and document public security tools and reusable CI workflows.
- Speaker: BSides Dayton and COISSA, 2026.
- Member of DEFCON 614. With the Call Center Village, where I volunteer.
Creator and teaching work
I share cybersecurity knowledge with more than 500K followers across platforms because I want more people to have access to it. Knowledge is power. Money is power. When you put knowledge behind a price tag, you help keep that power with the people who already have money. I have an ethical issue with that, so I open source a lot of my work and share what I learn.
Educational content focused on giving aspiring tech and cybersecurity professionals practical, real-world knowledge:
- Linux as a daily driver and production environment
- Cybersecurity investigations and real-world threat and news breakdowns
- Radio and Meshtastic communications and mesh networking
- Endpoint security and enterprise tooling deep dives
- Home labs and networking architecture and implementation
- Device reviews, privacy tools, and open-source infrastructure
Whether you're just starting out or leveling up, the goal is content that's accessible, practical, and security-focused.
You’re not dead until you stop learning. Happy hacking.
Outside work
- Amateur radio operator, General class license
- Ordained Priest, Church of the Latter Day Dude. I can secure the network and officiate the wedding afterward.
Contact
References, job history and a phone number are available to prospective employers on request. How to reach me, on the About page.
Find me online: LinkedIn